This week
Business
Individual
Partners
Intelligence
How we work
Sign in Check my firm
AI-driven · Evidence-grade exposure management

Attackers read your firm from outside. We read it first.

AI-powered attacks need AI-powered defense. AI lets anyone find a forgeable email domain, a look-alike or an exposed login in minutes. LeakTrace uses AI to find every way into your firm first, proves every finding and closes it before it is used.

One public DNS lookup, read-only. Nothing you type is kept.

Read-only, from outside Proof for every finding Every assessment human-verified Continuous exposure watch
The outside watch · LiveUpdated hourly
Look-alike domains checked
193.7K
And counting
Certificate records read185.5K
Actively exploited flaws watched1,734
Public disclosures indexed5,252
Firms read from outside2,589
Counted from our own records, 5 Oct, 17:11 UTCRead-only
The difference

Proof, not scores.

Every finding we show carries the record behind it and a check anyone can re-run, your insurer included. Human-verified before it reaches you.

Finding 01 · harbor-legal.exampleIllustrative · fictional firm
Closed
Finding
High

A stranger can send email as harbor-legal.example, and nothing stops it.

A forged payment request in the firm’s name could reach its clients’ inboxes.

EvidenceThe record, read from outside
Record: _dmarc.harbor-legal.example · TXT
$ dig TXT _dmarc.harbor-legal.example +short
"v=DMARC1; p=none"

Observed: p=none asks receiving servers to take no action, so mail forged in the firm’s name is not stopped.

Re-run it from any terminal. So can your insurer.

Fix
Record change · _dmarc.harbor-legal.exampleRe-checked from outside
"v=DMARC1; p=none"
"v=DMARC1; p=reject"

Switched on in one click where we can reach the firm’s DNS host; where we cannot, the exact record to publish, re-checked until it is closed.

Human-verified · within 72 hoursEvery paid assessment, before it is released. Every release written to the evidence log, verified daily.
  1. 01Proof, not scoresEvery finding carries its record and a check anyone can re-run.
  2. 02Human-verifiedEvery paid assessment human-verified before release, inside 72 hours.
  3. 03We close itForged email closed in one click where we reach your DNS host; the exact fix for the rest.
  4. 04First to knowRe-checked every hour, 24/7, on monitoring, with alerts within the hour.
  5. 05IndependentPaid by no one who sells the fixes, so every finding is there because it is true.
Your firm, from outside

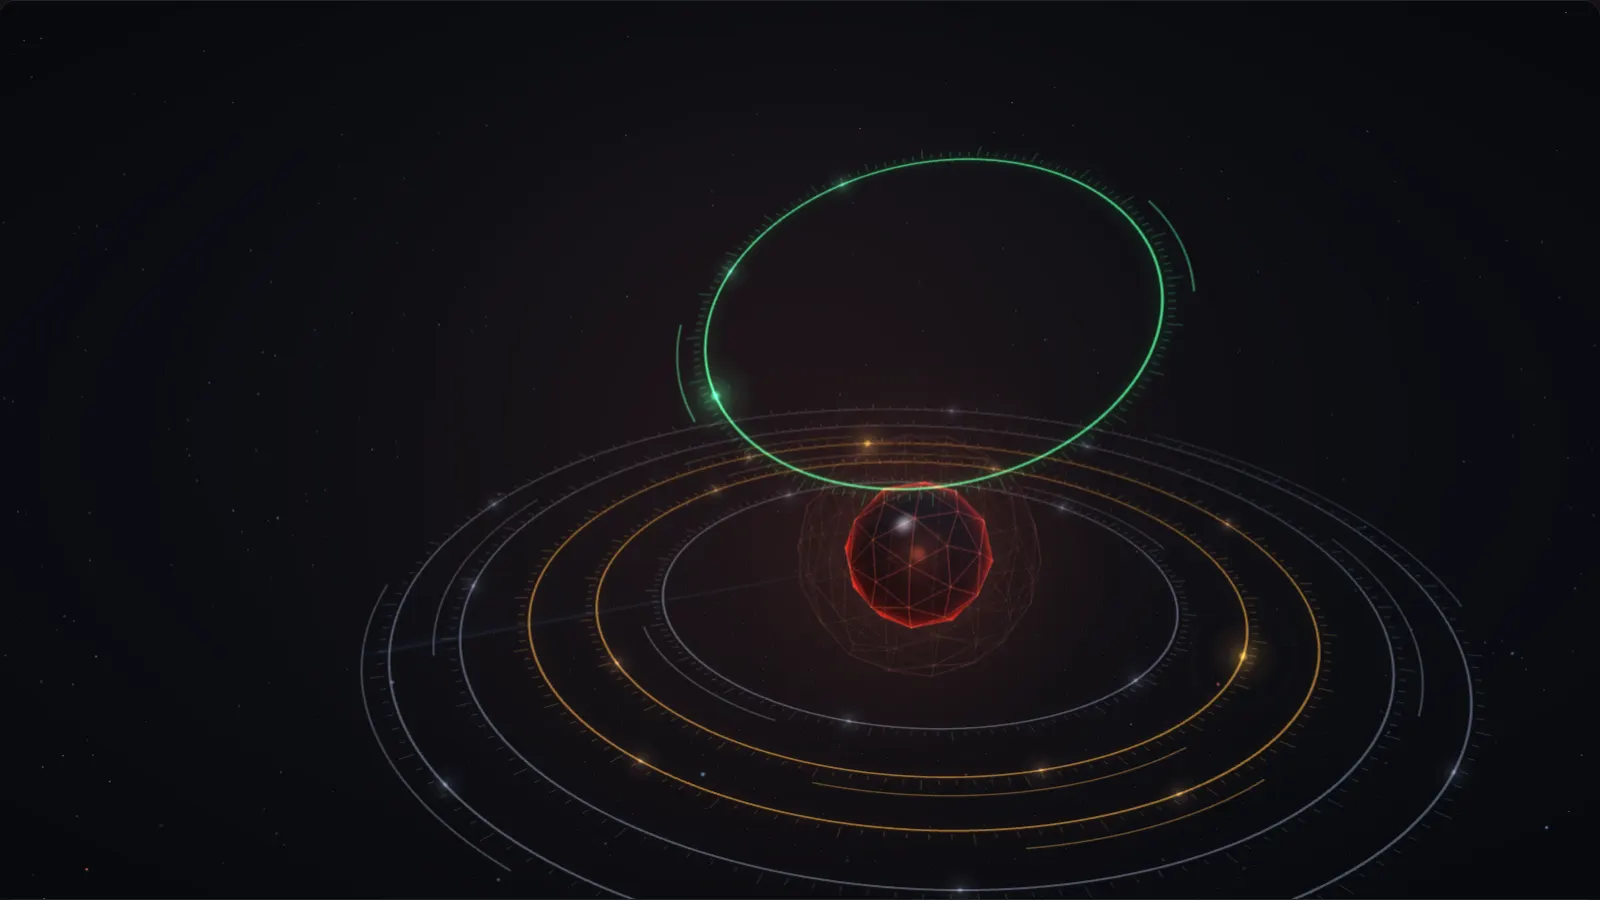
Every way in, pulled apart.

The surfaces an attacker’s AI tools read first, layer by layer, with the proof for each and the fix that closes it.

Drag to turn it. Illustrative firm.

Illustrative view of a fictional firm, harbor-legal.example: a glowing core inside six rings, one for each outside surface. The mail records ring is pulled out and shown closed.
harbor-legal.exampleIllustrative · fictional firm

Monitor: re-checked every hour, 24/7, on monitoring, with alerts within the hour. You are first to know.

Mail records · the recordOpenClosed
$ dig TXT _dmarc.harbor-legal.example +short
"v=DMARC1; p=none"
"v=DMARC1; p=reject"
Re-checked from outside
Human-verified · within 72 hours
  1. 01
    Mail recordsSPF · DMARC · DKIMp=none · forged mail deliveredp=reject · re-checked from outside
    Closed
  2. 02
    WebsiteHeaders · software versions · certificate
    Clear
  3. 03
    Look-alike domainsNames one letter off yoursharbor-legai.example · registered, resolvingTakedown request drafted, ready to send
    Open · fix ready
  4. 04
    Breach databasesFirm addresses in monitored breach databases3 firm addresses presentThe exact steps, address by address
    Open · fix ready
  5. 05
    Sign-in pagesPortals and admin pages anyone can reach
    Clear
  6. 06
    AI assistantsWhat AI assistants say about the firm
    Clear
The ways in that matter most

How firms are hit today, and our answer to each.

Three of the seven covered fully from outside, three in part, and the one we cannot see, we name.

The way inOur figureWhat we doCoverage
Email forged in your nameFake invoices and changed bank details, sent as you.
8 in 10professional firms cannot stop a stranger sending email in their name.LeakTrace Research · Measured 19 Sep 2026
  • Discover: the setting that lets forged mail through.
  • Validate: with the record, re-run from any terminal.
  • Close: in one click where we reach your DNS host; the exact record where we cannot.
  • Monitor: re-checked every hour.
CoveredFrom outside, end to end.
Stolen or reused passwordsA firm address in a breach database, and a password used again.
2 in 10professional firms have a shared address such as info@ in monitored breach databases.LeakTrace Research · Measured 30 Sep 2026
  • Discover: which firm addresses appear, with the source and date of each.
  • Monitor: re-checked every day.
Covered
Look-alike domains used to impersonate youA name one letter off yours, registered and live.
4 in 10professional firms have a look-alike of their domain registered and live.LeakTrace Research · Measured 30 Sep 2026
  • Discover: each one found and named.
  • Close: a takedown request drafted, ready for you to send.
  • Monitor: watched every hour.
Covered
Known flaws attackers are exploiting nowNewly listed flaws in the software a website runs.
The actively exploited flaws we watch for, counted live at the top of this page
  • Discover: matched to the software your website shows, within a day of being listed.
  • Monitor: every new listing, every day.
PartlyYour website only.
Exposed sign-in pages and remote accessPortals, admin pages and remote-access ports anyone can reach.
  • Discover: which sign-in pages answer from outside, and which remote-access ports are open on your website’s host.
PartlyWhether multi-factor sign-in is on is a question for your IT provider, and we say so.
AI-written phishing and impersonationMessages written for the person who opens them.
  • Close: email forged in your name, as above.
  • Validate: what AI assistants tell clients about your firm, checked against your own site, with a wrong answer flagged.
PartlyA convincing message from another address reaches people, not settings, and we say so.
RansomwareArrives through the ways in above.
  • Close: the outside ways in.
Not visible from outsideBackups and internal systems are out of sight from outside, and we say so.

Figures are LeakTrace Research, measured across the firms we have assessed, each with its date. Everything here is read from outside, from public sources only.

There’s only one answer to AI-powered attacks: AI-powered defense.

See one finding

One finding, read from outside, proven, human-verified and closed.

Captions on, no sound. Illustrative firm.

Read the transcript
  1. There's only one answer to AI-powered attacks. AI-powered defense.
  2. Attackers read your firm from outside. We read it first.
  3. What a score-only rating hands you: 62/100 · Grade C · “Improve your email security.” No record behind it. Nothing to re-run. No one signed it. A grade to trust, not a fix. What we hand you: A stranger can send email as harbor-legal.example, and nothing stops it.
  4. Proof, not scores. $ dig TXT _dmarc.harbor-legal.example +short returns "v=DMARC1; p=none". Every finding carries its record. Re-run it from any terminal. So can your insurer.
  5. Approved by a person · inside 72 hours. Every release written to the evidence log.
  6. "v=DMARC1; p=reject" · Re-checked from outside. Forged email: one click, where we reach your DNS host. The exact fix for everything else.
  7. Re-checked every hour, 24/7. Alerts within the hour.
  8. AI-driven · Evidence-grade exposure management. Proof, not scores. Check my firm · getleaktrace.com
The good news

The ways in are knowable, and closable.

Attacks on firms like yours still start from what the internet can see, and every one of those openings can be found from outside first.

24/7 Monitored day and nightRe-checked every hour on monitoring
1 h First to knowAlerts within the hour on hourly checks

Figures are LeakTrace Research, measured across the firms we have assessed, each with the date it was measured. Read the studies.

Why LeakTrace

Ahead of the attack, not after it. Every way into your firm, found first, proven and closed.

See the outside watch
193.7K

Look-alike domains checked

Brand impersonation caught within the hour it goes live, on monitoring.

185.5K

Certificate records read

New host names on your domain found as they are certificated, re-checked hourly on monitoring.

2,589

Firms read from outside

Each read the way an attacker’s tools read it, from public sources, logged into nothing.

Counted from our own records as of 5 Oct 2026, 17:11 UTC, refreshed hourly.

Illustrative · fictional firm

One morning on the watch. Discovered, validated, closed.

What a partner sees on a fictional firm, harbor-legal.example, as the watch finds a way in and closes it.

  1. 01Discover
  2. 02Validate
  3. 03Close
  4. 04Monitor

Introducing the outside watch

Continuous exposure watch, AI-driven and read from outside, in four stages: Discover, Validate, Close and Monitor. The next machine-speed attack finds the door already shut.

Discover every way in

Every way into your firm, discovered from outside the way an attacker’s tools read it. Nothing to install, no access to give.

6Exposure classes watched, from forged email to AI answers
HourlyEmail settings, look-alikes and new host names re-checked, on monitoring
What we monitor
Email impersonationEvery gap that lets a stranger send email as your firm, found and closed
Brand impersonationLook-alike domains caught within the hour they go live, with a takedown drafted
Attack surface discoveryEvery new system exposed on your domain, found as it appears
Exploited vulnerabilitiesFlaws attackers are actively using, matched to your website’s software within a day
Credential exposureYour firm’s addresses in breach data, flagged before the passwords are reused
AI reputationWhat AI assistants tell clients about your firm, and every wrong answer flagged

Validate every finding

The exact record behind each finding, a check anyone can re-run, and human verification before release. Every paid assessment carries a signed record anyone you hand it to can verify in one step.

100%Of paid assessments human-verified before release
72 hFrom confirmation to an approved assessment
Verify a record
Evidence for every findingThe exact record, header or listing behind it
Signed assessment recordDated, and verifiable by anyone you hand it to
Tamper-evident recordEvery approval, alert and DNS change hash-chained and verified daily
Anti-impersonation checkAnyone can confirm in one step that a message really came from us

Close the way in

Forged email, the opening we find most, closes in one click where we reach your DNS host: staged, re-checked, nothing changed until you confirm. Your IT provider gets the exact fix for the rest, re-checked until it is closed.

1 clickProtects your firm against forged email in its name, where we reach your DNS host
1,734Actively exploited flaws watched for, matched to your website’s software on monitoring
How it works
One-click email fixWhere we can reach your DNS host; the exact records where we cannot
Takedown request draftedFor each live look-alike, for you to send
Patch before it is usedNewly exploited flaws matched to your software, with the fix
Insurance questions pre-filledThe outside questions on your cyber application, with the evidence

Monitor around the clock

Re-checked every hour, 24/7, with alerts within the hour. You are first to know, before a client, a bank or an insurer.

1 hAlerts within the hour on hourly checks, by email, Slack or Teams
24/7Monitored day and night; the same day for daily checks
For firms
Alerts within the hourThe way in, in plain words, within the hour on hourly checks and the same day on daily ones
Slack or TeamsAlerts where your partners already talk, or by email
Board-ready summaryBoard-ready exposure summary, every month
Peer benchmarkYour exposure ranked against firms in your sector, where 30 or more are measured

So you see it first, at speed and scale.

Patch before it is used against you. Take down a look-alike before it sends its first invoice. Close the way in before anyone walks through it.

Counted from our own records as of 5 Oct 2026, 17:11 UTC. Illustrative items are labelled.
1 clickTo protect your name against forged email, where we can reach your DNS host
Newest on the exploited list
Citrix NetScalerAdded 4 Oct · Citrix NetScaler Improper Restriction o…
Zammad GmbH ZammadAdded 2 Oct · Zammad GmbH Zammad Session Fixation Vul…
Zammad GmbH ZammadAdded 2 Oct · Zammad GmbH Zammad Improper Privilege M…
1 dayTo match a newly exploited flaw to the software a monitored firm’s site shows
5,252Public disclosures indexed, each with the way in. Updated daily
2,570Firms whose addresses were checked against monitored breach databases
72 hFrom confirmation to a human-verified assessment
Illustrative
001$ dig TXT _dmarc.your-firm.com
002;; ANSWER: 0
003$ dig TXT your-firm.com
004"v=spf1 include:mail ~all"
005$ dig +short MX your-firm.com
0Log-ins to any client system. Every check is a public lookup, like this one.

Built for the AI era. Enterprise-grade, for firms of every size.

AI reputation

What AI assistants tell your clients about you

We ask an AI assistant what it says about your firm, check the phone number it gives against the pages it cites, and flag a wrong answer.

One click

Forged-email protection, switched on

From outside, where we can reach your DNS host. Staged, re-checked, nothing changed until you confirm.

Within a day

Exploited flaws matched to your website

Newly listed, actively exploited flaws matched to the software your site shows.

Verified daily

A tamper-evident record

Every approval, alert and DNS change hash-chained, and the chain verified every day.

Every look-alike

A takedown request, drafted

For every live look-alike of your domain, ready for you to send.

Pre-filled

Your insurance questions, answered

The outside questions on your cyber application, pre-filled with the evidence behind each answer.

15 seconds

A personal video of your own finding

Where your firm has a forged-email finding, it is on screen, its proof re-run the day the video is made.

Research-driven. Fix-ready.

LeakTrace Research and the Disclosure Tracker

Every figure measured by us across the firms we have assessed, dated, and the same reading drives the exposure watch on your firm.

Open the Disclosure Tracker
What forged email already costs
$3,046,598,558

Reported losses to business email fraud in the United States in one year. 24,768 complaints, 2025.

Source: FBI IC3 2025 Internet Crime Report, business email compromise, 2025. Reported losses only.

The latest · 5 Oct 2026

How they got in this week, and what we watch for you.

Public source2 Oct 2026SecurityWeek

US think tanks and universities

How they got in
Email made to look like it came from a trusted sender.
What we watch
Whether anyone can send email that passes as your domain.
Public source2 Oct 2026BleepingComputer

Frontline Education

How they got in
A supplier or vendor that was compromised first.
What we watch
The outside services your domain depends on.
Public source1 Oct 2026DataBreaches.net

Victims across the US and Puerto Rico

How they got in
A known flaw in software the victim ran.
What we watch
Software versions your site advertises and known flaws in them.

Every finding mapped to the rule you answer to

FTC Act Section 5US

Safeguard consumer data. Failures are treated as unfair or deceptive practices.

FTC Safeguards RuleUS

Tax preparers, mortgage brokers and other financial institutions: multi-factor sign-in, and notice to the FTC within 30 days of a breach of 500 or more people.

HIPAAUS

Covered clinics: protect patient health information and tell patients within 60 days of discovery.

State breach notification lawsUS

Notify affected people when personal information is exposed. Timing varies by state.

201 CMR 17.03US

Anyone holding a Massachusetts resident's data: review the written security program every year.

PIPEDACA

Safeguards appropriate to the sensitivity of the information. Notify of a breach that creates a real risk of significant harm, and keep a record of every breach for 24 months.

Alberta PIPACA

Prompt notice to the Commissioner where harm is a real risk.

BC PIPACA

Reasonable security arrangements against unauthorized access.

PHIPACA

Ontario health custodians: protect patient information and notify the Information and Privacy Commissioner of breaches.

Your country’s rules first. Only the rules the Rules and Insurance Briefing maps, each listed only where its applicability can be stated honestly.

Independence

Outside only. Independent, and answerable to you.

We read what your firm shows to the public internet, and nothing else. What we find goes to you alone.

Your IT provider keeps your systems running. We hand them an independent list, each finding with its evidence and the change that closes it.

A penetration test needs access to try to break in. We read only what is already public, and log into nothing.

Your insurer’s scan feeds your premium. We show you the same outside view first, so you walk into renewal knowing the answers.

Access neededNone
Log-ins to your systemsNone
Mutual NDAAvailable on request
Questions
Nothing of yours. We read what your firm shows to the public internet, the way an attacker’s tools would.

The incidents that reach firms like yours, and what to check, in one email.

One email when a briefing is published. Unsubscribe in one click. Privacy

See what your firm looks like from outside.

Your outside reading: every way in we can see, found before anyone uses it. Free, read-only, sent only to you.

What we readPublic sources only
Who sees itYou alone
Delivery72 hours from confirmation
Mutual NDAAvailable on request

A person reads every request. We reply within one business day from [email protected]. Privacy